Best Practices for Implementing ISO 27001
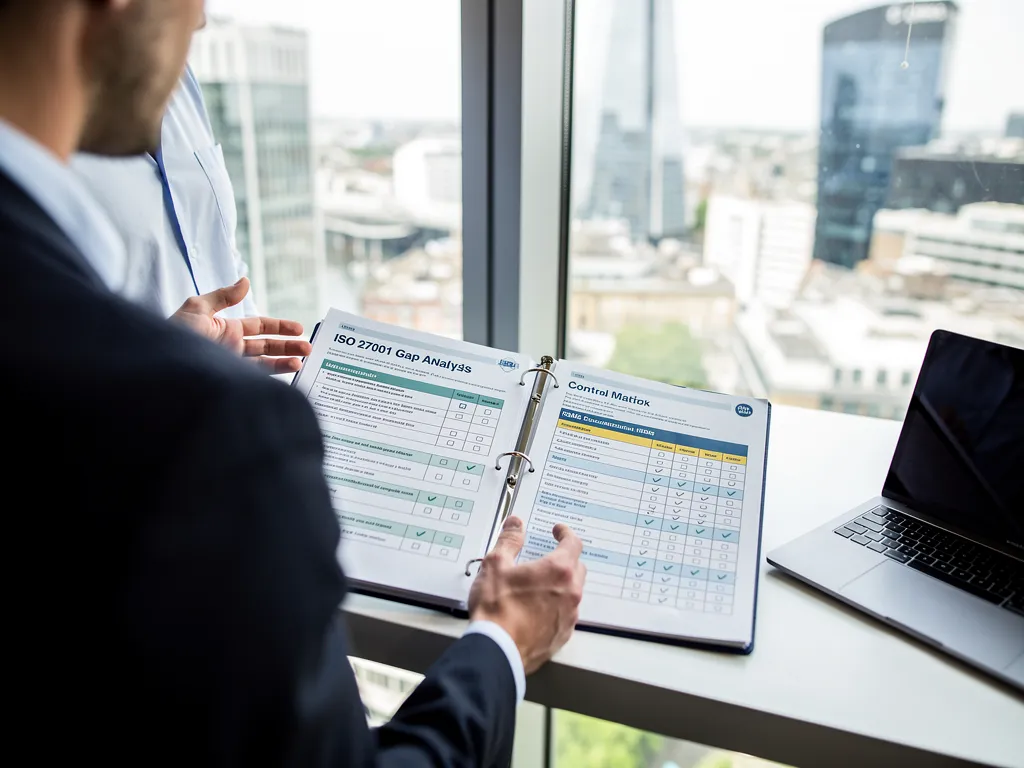
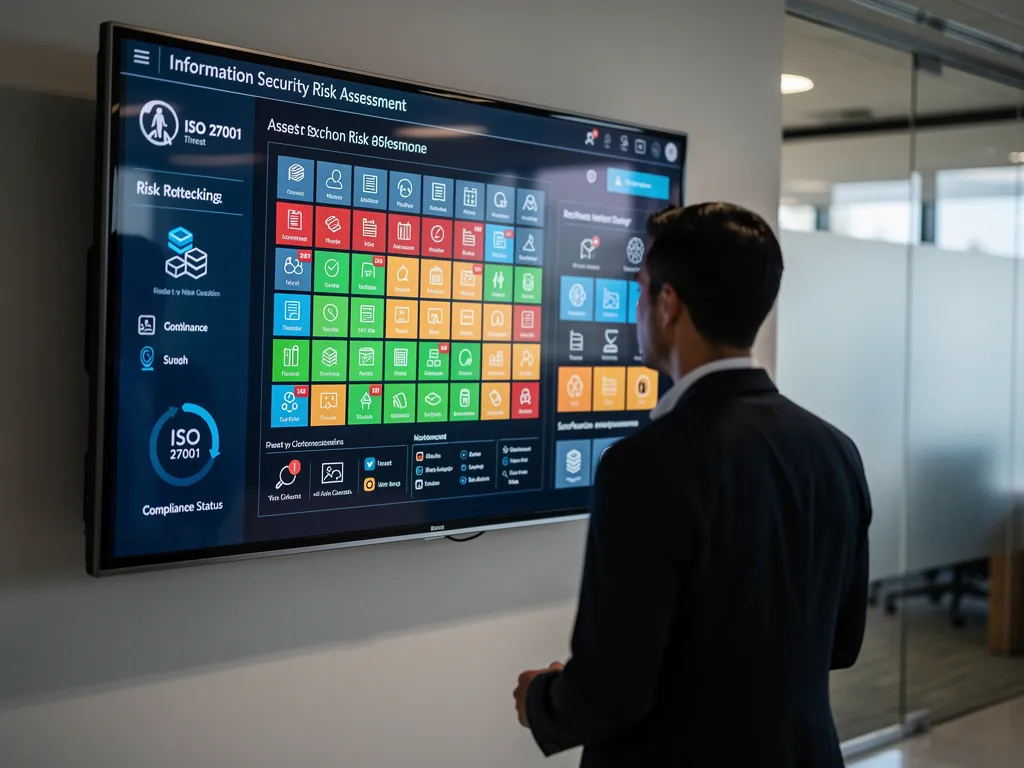
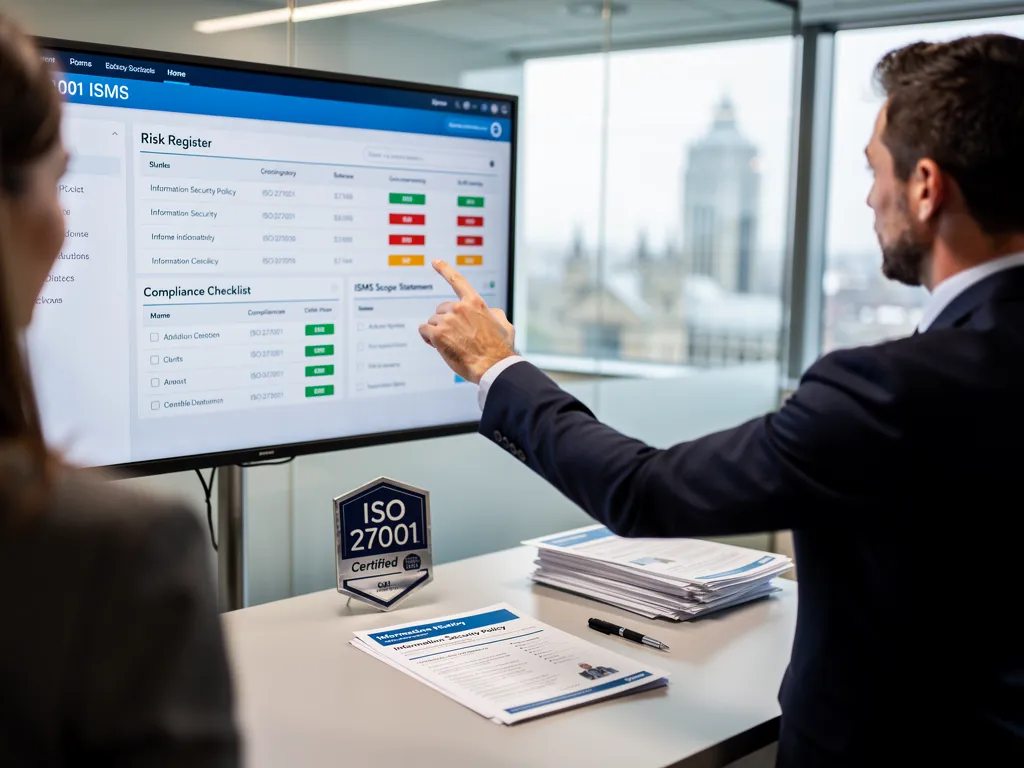
Implementing ISO 27001 can be a complex process, but following best practices can streamline the journey. Organizations should start by conducting a thorough risk assessment to identify vulnerabilities and establish security controls tailored to their specific needs.
Additionally, fostering a culture of security awareness among employees is crucial. Regular training sessions and clear communication regarding security policies can significantly enhance compliance and effectiveness in maintaining ISO 27001 standards.
The Role of Continuous Improvement in ISO Certifications
Continuous improvement is a fundamental aspect of maintaining ISO certifications, including ISO 27001. Organizations must regularly review and update their information security management systems (ISMS) to adapt to evolving threats and regulatory changes.
Utilizing feedback from audits and employee suggestions can provide valuable insights into potential improvements. By embracing a mindset of ongoing enhancement, companies can ensure their ISMS remains robust and effective over time.
Common Challenges in Achieving ISO 27001 Certification
Achieving ISO 27001 certification presents several challenges that organizations must navigate. Common obstacles include resistance to change within the workplace, insufficient resources, and lack of management support, which can hinder the implementation of necessary security measures.
To overcome these challenges, it is essential to engage stakeholders at all levels and allocate adequate resources for training and technology. By addressing these issues proactively, organizations can improve their chances of successful certification.
The Benefits of ISO 27001 Certification for Businesses
ISO 27001 certification offers numerous benefits for businesses, including enhanced credibility and trust with clients and partners. By demonstrating a commitment to information security, organizations can differentiate themselves in the marketplace and attract new customers.
Moreover, achieving this certification can lead to improved operational efficiencies and reduced risk of data breaches, ultimately saving costs associated with security incidents. The long-term value of ISO 27001 extends beyond compliance, fostering a culture of security within the organization.