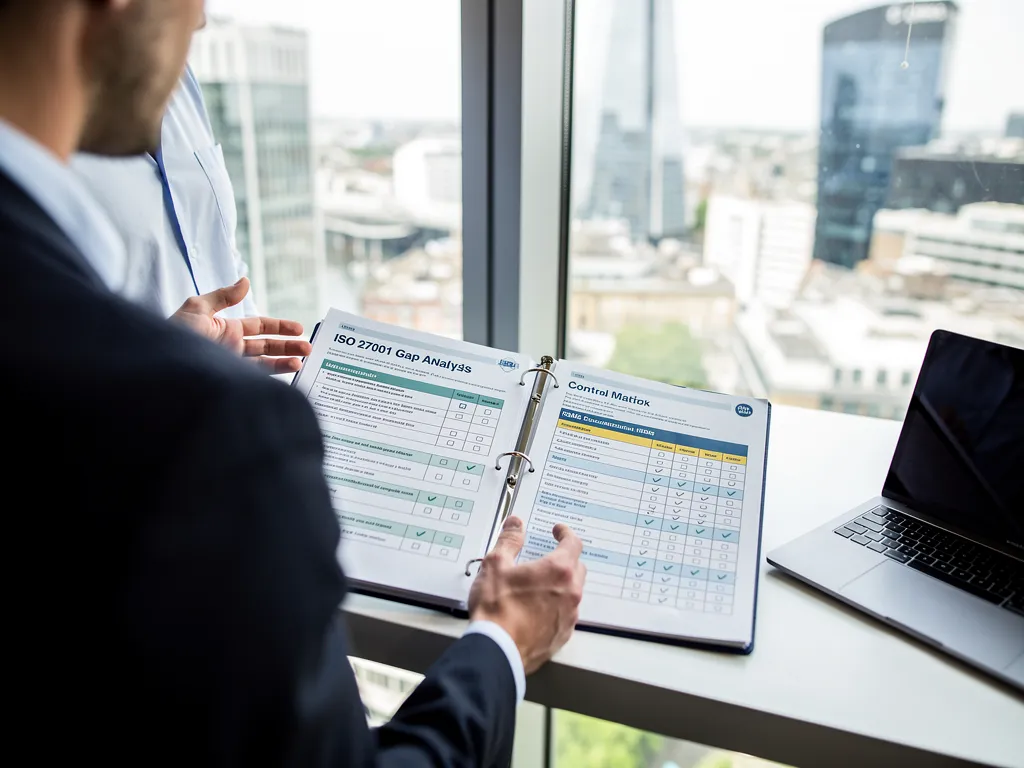
An ISO 27001 gap analysis is a focused compliance assessment that compares an organisation’s existing information security management system (ISMS) and practices against the requirements of ISO 27001:2022, identifying missing controls, documentation gaps and weaknesses that block certification readiness. This guide explains how a gap analysis works, why it matters for compliance and risk reduction, and how to convert findings into a practical remediation roadmap. Readers will learn a step-by-step gap analysis process, common methodologies (including controls-mapping and risk-based approaches), realistic cost drivers and budgeting guidance, plus prioritisation techniques to turn gaps into measurable workstreams. The article also includes practical checklists, comparison tables and a prioritisation template you can use immediately. Throughout, keywords such as ISO 27001 gap analysis, ISMS gap analysis, security assessment and gap analysis methodology ISO 27001 are woven in to help practitioners, auditors and information security teams quickly apply insights and prepare for certification or internal improvement.
What Is ISO 27001 Gap Analysis and Why Is It Important?
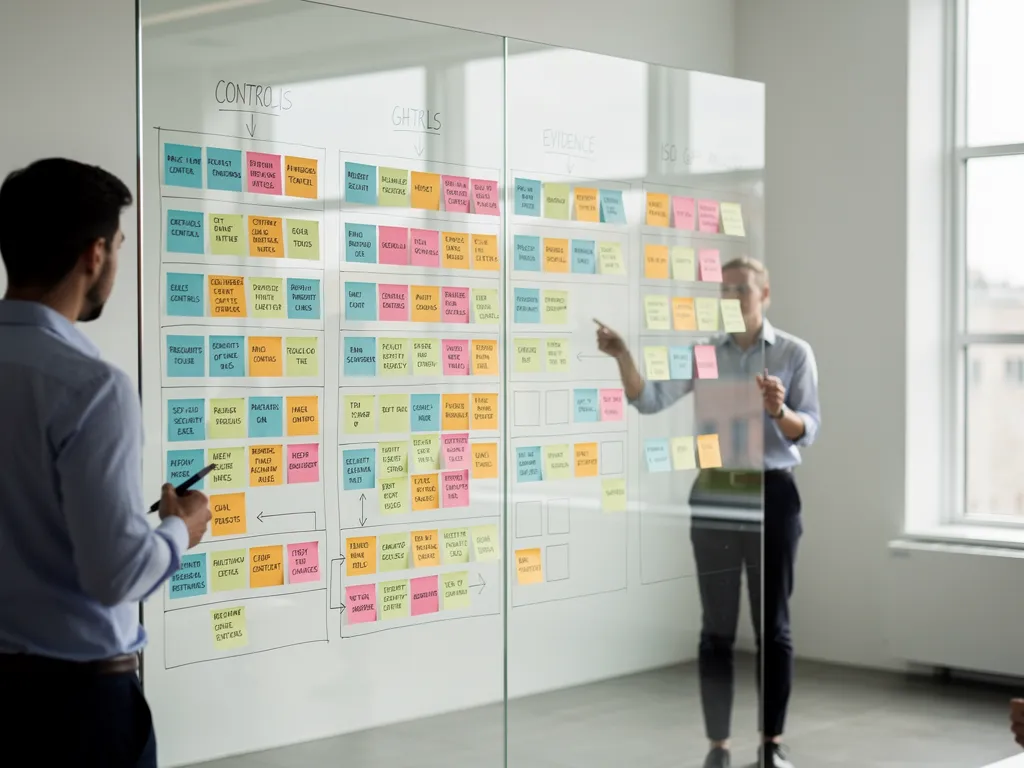
An ISO 27001 gap analysis is a diagnostic assessment that maps current security controls and documentation to ISO 27001 clauses and Annex A controls, revealing discrepancies between practice and standard requirements. The mechanism involves control mapping, evidence collection and scoring so organisations understand where they lack policy, process, or technical controls; the specific benefit is clarity on remediation effort and prioritised actions to reduce risk. Performing a gap analysis shortens certification timelines, reduces unexpected audit findings, and focuses limited resources on high-impact controls. Understanding this difference between a gap analysis and an audit—where the former is formative and the latter is conformance-focused—helps organisations plan remediation before a formal assessment.
How Do We Define ISO 27001 Gap Analysis?
A gap analysis for ISO 27001 systematically evaluates an organisation’s ISMS components—scope definition, policies, procedures, Statement of Applicability (SoA), and control implementations—against ISO 27001 requirements to identify missing or inadequate items. It works by mapping each requirement and Annex A control to existing evidence, interviewing process owners, and scoring gaps by severity and evidence strength, producing a gap register. This diagnostic phase differs from an internal audit in that it is forward-looking and advisory rather than compliance-judgmental, and it often includes suggested remediation actions and timelines. Clear scope definition and evidence sampling are essential to keep the analysis efficient and targeted.
What Are the Key Benefits of Conducting an ISO 27001 Gap Analysis?
Improved Certification Readiness: Identifies showstopper issues before formal audit, reducing rework.
Prioritised Remediation: Links gaps to risk and business impact so teams fix what matters first.
Cost Efficiency: Avoids unnecessary controls by focusing resources on high-priority remediation.
Faster Time-to-Compliance: A clear roadmap shortens the path from current state to certified ISMS.
These benefits make the gap analysis a practical first step; with identified gaps and priorities, organisations can proceed to a risk treatment plan and SoA update.
For organisations that prefer external support, booking a free consultation to review gap analysis objectives can provide independent validation and a tailored plan to accelerate remediation while preserving internal resources.
What Are the Essential Steps in an ISO 27001 Gap Analysis Process?
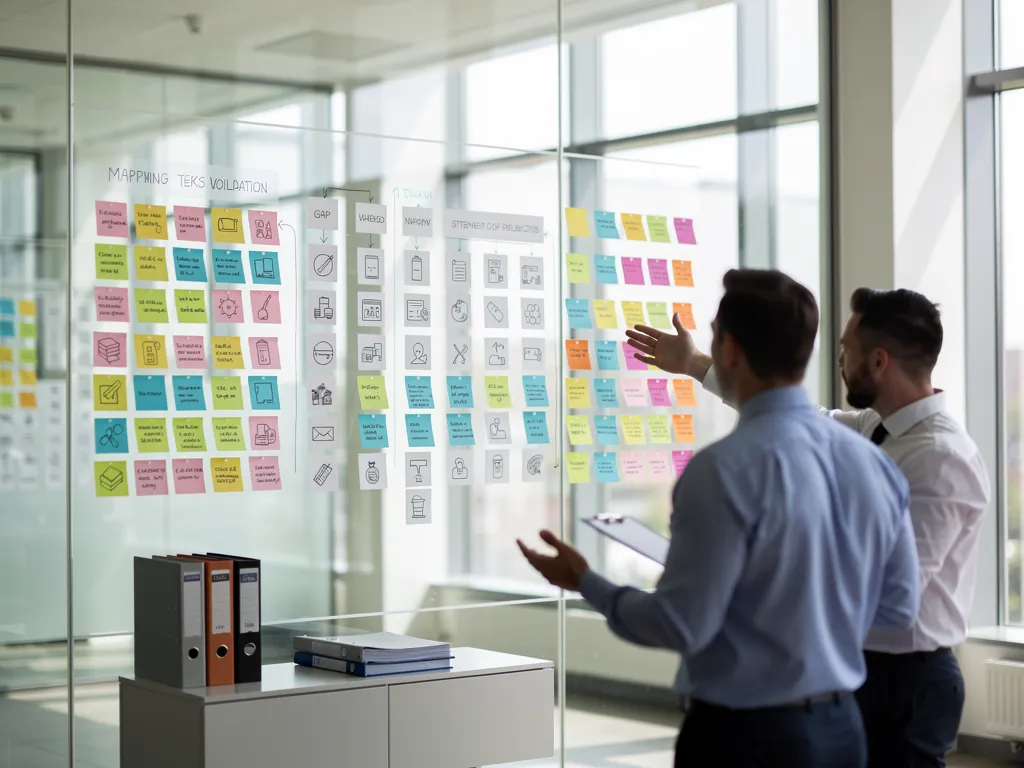
An effective ISO 27001 gap analysis follows a defined sequence: scoping, documentation review, control mapping, evidence validation, risk-based scoring and reporting with remediation recommendations. The mechanism links evidence to ISO clauses and Annex A controls, and the specific benefit is a ranked list of actions aligned to business risk and compliance urgency. Deliverables normally include a gap register, draft SoA, and an improvement roadmap with owners and estimated effort. Clear roles—information owners, security lead, internal audit and optional external advisers—ensure the process runs smoothly and that remediation responsibilities are actionable.
How Do You Prepare for an ISO 27001 Gap Analysis?
Preparation begins by defining scope and objectives, assembling an asset inventory and gathering existing ISMS documentation such as policies, procedures, incident records and previous assessments. Preparation also designates stakeholders and sets a realistic timeline so evidence collection and interviews are scheduled with system owners.
Scope statement
Asset list
Current SoA (if present)
Access to key systems for sampling
Effective preparation reduces consultant hours and internal disruption while improving the accuracy of findings.
What Are the Main Activities During the Gap Analysis?
During analysis, practitioners map controls to Annex A, review documentation and evidence, interview process owners to validate practices, and score each gap by severity and evidence sufficiency. Typical artefacts produced are a control matrix, evidence log and preliminary risk scoring that feed into a draft SoA and remediation plan.
Evidence sampling may include configuration screenshots, system logs, policy sign-offs and training records; a consistent scoring rubric makes prioritisation transparent.
These activities culminate in a formal gap report that recommends corrective actions, owners and timelines.
For teams that lack internal capacity, specialist advisers and information hubs can support scoping, documentation review and risk assessment tasks—book a free consultation to determine which steps would benefit most from external expertise and to obtain a tailored engagement plan.
Which Methodologies Are Used for ISO 27001 Gap Analysis?
Gap analyses commonly adopt three methodological approaches: a checklist-based control mapping, a risk-based assessment that prioritises by likelihood and impact, or a hybrid/maturity approach combining control presence with maturity scoring. Each methodology uses the same core entity—Annex A and ISO clauses—but differs in attribute focus: presence vs severity vs maturity. Choosing the right method affects work effort and outcome clarity, so selection should align with certification objectives, resource availability and risk appetite.
Methodology | Focus / Typical Activities | When to Use / Pros & Cons |
|---|---|---|
Checklist (controls-mapping) | Systematic mapping of Annex A controls to evidence and documentation | Use for quick baseline; low cost, but may miss risk context |
Risk-based | Score gaps by likelihood × impact and recommend treatment priorities | Use when prioritisation by business risk is required; more accurate outcomes but needs risk expertise |
Maturity assessment (hybrid) | Assess both presence and maturity of controls (process, technology, people) | Use for improvement roadmaps; provides long-term planning but is more time-consuming |
This comparison helps teams pick an approach that balances speed, depth and business relevance. The next important consideration is the specific techniques used to discover gaps.
What Are the Common Techniques for Identifying Gaps?
Common identification techniques include structured checklists, interviews and process walkthroughs, evidence sampling and automated discovery or vulnerability scanning where applicable. Checklists map controls to evidence, interviews validate how processes operate day-to-day, and automation can highlight technical misconfigurations or missing patches. Combining techniques yields the most reliable results: human interviews provide context while automated scans surface technical issues. Outputs typically include a gap register, evidence log, and control matrix for reporting.
How Is Risk Assessment Integrated into the Gap Analysis?
Risk assessment integrates by assigning each identified gap a likelihood and impact score, producing a risk severity rating that informs remediation priority and cost-benefit decisions. A simple risk matrix (e.g., 1–5 likelihood × 1–5 impact) converts observations into prioritised actions and links directly to the SoA and risk register. High-severity gaps become immediate remediation targets, while low-severity items can be scheduled for later sprints or monitored. Updating the SoA and risk register after the analysis ensures the ISMS reflects current risk posture and treatment decisions.
How Much Does an ISO 27001 Gap Analysis Cost?
Cost for an ISO 27001 gap analysis depends on scope, depth, organisation size and whether external consultants or internal teams perform the work; primary cost drivers include the number of systems in-scope, number of locations, evidence readiness, and necessary specialist testing. The mechanism determining price is largely effort-driven—more assets, more interviews and deeper technical testing increase consultant days or internal effort, and the specific benefit of clarity on cost drivers helps teams budget effectively. Typical ways to reduce cost include phased delivery, pre-engagement preparation and focusing external consultancy on the most technical or highest-risk steps.
Before presenting example ranges, the following table clarifies cost components and estimated impacts on budget planning.
Cost Driver | Description | Estimated Range / Example Impact |
|---|---|---|
Scope size | Number of systems, business units and locations in scope | Small scope reduces effort; large enterprise multiplies days required |
Evidence readiness | Availability of policies, logs and proof of control | Higher readiness reduces consultant hours; low readiness increases costs |
Depth of testing | Need for technical testing, penetration scans or tool-based discovery | Adds specialist day rates and tool costs; increases overall budget |
Consultancy level | Day-rate vs fixed-price, junior vs senior resource | Senior specialists cost more but speed up delivery and quality |
This table highlights that costs are not fixed and should be scoped before firm pricing. For a tailored quote aligned to your organisation’s scope and evidence posture, consider booking a free consultation to get a realistic, written estimate and recommended phased approach.
What Factors Influence the Cost of ISO 27001 Gap Analysis?
Detailed cost influencers include the breadth of scope (single site vs multi-site), complexity of IT environment (cloud, legacy systems), how much documentation exists and whether specialist tools or penetration testing are required. Internal resource availability affects cost because more in-house preparation reduces consultant hours, while evidence unavailability increases time to collect artefacts. These factors combine to determine whether a fixed-price engagement is feasible or a day-rate approach is more appropriate. Understanding these drivers enables more accurate budgeting and procurement.
How to Budget Effectively for a Gap Analysis?
Budget effectively by scoping the engagement, preparing documentation in advance and choosing a phased delivery model that splits baseline assessment, remediation planning and follow-up verification into separate tranches.
Estimated consultant days
Internal staff time
Tool or scanning costs
Remediation effort estimates
Phase one can be a low-cost baseline with subsequent paid phases for remediation support. Where budgets are constrained, focus initial effort on high-risk systems to gain the best security return on investment. Requesting a tailored quote after a preparatory scoping call will reduce surprises and help plan cashflow.
How Can You Identify and Prioritize Areas for Improvement After a Gap Analysis?
Turning gap findings into an actionable roadmap requires a prioritisation framework that combines risk severity, business impact, ease of implementation and compliance urgency. The mechanism is a scoring matrix that converts qualitative observations into ranked remediation items; the specific benefit is an evidence-based sequence of actions that balances risk reduction with resource realities. A practical improvement plan assigns owners, deadlines, effort estimates and success metrics so progress is measurable and auditable. Use the following template table to score and prioritise identified gaps based on risk severity and suggested actions.
Identified Gap | Risk Severity / Impact | Priority / Suggested Action |
|---|---|---|
Missing access control policy | High / Potential unauthorised access | Priority: High — Draft policy, implement role-based access controls within 3 months |
Lack of patching evidence | Medium-High / Exploit risk on public-facing systems | Priority: High — Implement patching schedule and evidence logs within 6 weeks |
Outdated training records | Medium / Increased human risk | Priority: Medium — Run targeted awareness training and monitor completion rates |
This template makes it straightforward to assign pragmatic actions and timelines. Once priorities are set, create SMART tasks and track progress to ensure remediation closes identified gaps.
What Criteria Determine the Severity of Identified Gaps?
Severity criteria typically combine impact (financial, reputational, operational), likelihood of exploitation, detectability and regulatory drivers; each dimension is scored to produce an overall severity rating. Business impact considerations, such as data sensitivity or contractual obligations, increase priority even if technical likelihood is low. Regulatory or contractual drivers (e.g., obligations to clients or regulators) can move medium-risk items to high priority. A transparent rubric ties remediation decisions to business objectives and risk appetite.
How to Develop an Improvement Plan Based on Gap Analysis Results?
Develop an improvement plan by converting each gap into a SMART remediation task with an assigned owner, clear deadline, estimated effort and measurable success criteria such as evidence artifacts or control tests. Use short-term sprints for high-priority items (quick wins) and longer initiatives for architectural changes; track progress via a remediation register and integrate updates into the SoA and risk register. Monitoring KPIs like percent complete, time-to-remediate and reduction in high-severity gaps keeps stakeholders informed and accountable. Regular review cycles ensure the plan remains aligned to evolving threats and business priorities. For organisations wanting hands-on support to convert gap registers into a delivery roadmap, consider scheduling a free consultation to review results and agree a practical remediation roadmap with expert input.
What Are Common Challenges in ISO 27001 Gap Analysis and How to Overcome Them?
Common challenges during gap analysis include incomplete documentation, limited stakeholder availability, scope creep and inconsistent evidence quality; each of these problems slows progress and undermines confidence in findings. Overcoming these obstacles requires governance—clear sponsorship, a defined scope, a documentation checklist and phased delivery to contain scope. The benefit of addressing these process problems early is accurate, defensible gap reporting that leads to achievable remediation.
What Obstacles Typically Arise During Gap Analysis?
Typical obstacles are unavailable or fragmented evidence, lack of executive sponsorship, competing priorities across business units and technical complexity for legacy or hybrid systems. The impact of these obstacles is delayed analysis, higher consultancy costs and unclear remediation priorities; solutions include assigning accountable owners, creating a central evidence repository and breaking the analysis into manageable phases. Problem/impact/solution pairs clarify immediate actions and keep momentum. Addressing evidence readiness and stakeholder engagement up front reduces rework and improves outcomes.
How Can Organizations Ensure a Successful Gap Analysis?
To ensure success, secure executive sponsorship, define a narrow and achievable scope, appoint process owners and prepare key documentation before the assessment begins. Maintain a consistent scoring rubric and evidence template, and schedule interviews with relevant owners to validate practices rather than rely solely on documents. Follow-up governance—tracking remediation, updating the SoA and scheduling verification—completes the improvement loop and supports future certification. When internal capability is limited, bringing in experienced advisers or using information hubs for structured guidance can accelerate delivery and increase confidence in results.
Practical checklist for success:
Define scope and objectives with executive sign-off
Gather and centralise documentation before assessment
Assign owners and realistic deadlines for remediation
Use a consistent scoring and prioritisation rubric
These steps ensure the gap analysis drives meaningful, measurable improvement and prepares the organisation for audits and certification.
Start with a clear scope and sponsor: Executive backing reduces resistance and secures resources.
Prepare evidence in advance: Centralised artefacts speed analysis and reduce cost.
Use a risk-based prioritisation: Focus on high-impact controls first and document decisions.
Remediation Phase | Task | Outcome |
|---|---|---|
Triage | Score gaps and assign priority/owners | Clear action list with owners |
Remediate | Implement controls, update documentation | Evidence for control effectiveness |
Verify | Internal audit or reassessment | Confirmed remediation and SoA update |
This phased model helps teams structure work and measure progress at each stage. If you need assistance structuring phases and estimating effort, a short consultation with an experienced adviser can provide a tailored plan.