ISO 27001 risk assessment is the structured process organisations use to identify information security risks, evaluate their likelihood and impact, and decide on proportionate treatments that protect confidentiality, integrity and availability. This article explains how ISO 27001 risk assessment fits into an ISMS, the practical steps from scoping to treatment, and the documentation auditors expect such as the risk register, Risk Treatment Plan (RTP) and Statement of Applicability (SoA). Readers will learn tangible methods for asset and threat identification, how to choose between qualitative and quantitative analysis, and concrete examples to populate a risk register so assessments are audit-ready. The guide also covers how to monitor emerging threats, incorporate AI/ML risk scenarios into registers, and keep the ISMS current through internal audit and management review. Finally, practical support options are described for organisations that want expert help to accelerate readiness and certification.
What Is ISO 27001 Risk Assessment and Why Is It Important?
ISO 27001 risk assessment is a formal activity within an ISMS to identify information assets, threats and vulnerabilities, determine risk levels, and guide control selection to reduce unacceptable risks. The mechanism links asset value and threat scenarios to impact and likelihood estimates so organisations can prioritise controls from Annex A and allocate resources where they reduce business risk most effectively. The immediate deliverables of a compliant assessment are a populated risk register, a Risk Treatment Plan describing chosen controls, and a Statement of Applicability explaining why Annex A controls are included or excluded. Performing this assessment supports regulatory compliance, demonstrates due diligence to stakeholders, and reduces the probability and business impact of cyber incidents. Organisations that document and maintain risk assessments show auditors and decision-makers a measurable rationale for control choices and continuous improvement.
What Does ISO 27001 Risk Assessment Involve?
ISO 27001 risk assessment involves establishing the assessment context, creating an inventory of assets with values, identifying threats and vulnerabilities, analysing likelihood and impact, evaluating risk against criteria, and documenting results in a risk register and RTP. The process begins by scoping the ISMS and defining risk criteria such as acceptable risk levels and business impact thresholds; these criteria steer later prioritisation. Practical activities include asset classification (data, systems, people), threat modelling (insider threat, supply chain compromise, ransomware, AI misuse), and vulnerability assessment (patch status, misconfigurations). A simple sample risk-register entry helps illustrate: Asset = Customer database; Threat = ransomware; Vulnerability = missing offline backups; Likelihood = medium; Impact = high; Treatment = mitigate with backups and segmentation. Clear documentation of decisions and ownership ensures traceability during audits and continuous reviews.
ISMS-CORAS: Structured Method for ISO 27001 ISMS Compliance Established standards on security and risk management provide guidelines and advice to organizations and other stakeholders on how to fulfill their security needs. However, realizing and ensuring compliance with such standards may be challenging. This is partly because the descriptions are very generic and have to be refined and interpreted by security experts, and partly because they lack techniques and practical guidelines. In previous work we showed how existing security requirements engineering methods can be used to support the ISO 27001 information security standard. In this chapter we present ISMS-CORAS, which is an extension of the CORAS method for risk management that supports the ISO 27001 standard. ISMS-CORAS comes with techniques and guidelines necessary for establishing an Information Security Management System (ISMS) compliance with the standard, as well as the artifacts that are needed for the required documentation.
Why Is Risk Assessment Critical for an Effective ISMS?
Risk assessment is the foundation of an effective ISMS because it directly informs which Annex A controls are necessary, how resources should be prioritised, and how management demonstrates continual improvement. Without a defensible risk assessment, control selection is arbitrary and auditors will question the organisation’s justification for excluding or accepting controls. Accurate assessment supports targeted controls that reduce incidents and minimise recovery costs, and it creates evidence for management review, supplier contracts and regulatory reporting. For example, a thorough assessment that identifies supplier-delivered software as a critical asset will drive supplier security controls and contract clauses, reducing third-party risk exposure. Maintaining this link between assessed risks and chosen controls is essential for certification readiness and long-term resilience.
A compliant ISO 27001 risk assessment produces a set of interlinked artefacts that auditors expect to see populated and maintained:
Risk register: the living record capturing each identified asset, its linked threat and vulnerability, assigned likelihood and impact ratings, and the chosen treatment.
Risk Treatment Plan (RTP): the document specifying selected controls, named owners, target timelines and success metrics for every risk requiring treatment.
Statement of Applicability (SoA): the record listing all Annex A controls, stating implementation status, and justifying each inclusion or exclusion.
Risk criteria: the defined acceptable risk levels and business impact thresholds that steer prioritisation throughout the assessment.
Annex A controls: the catalogue of candidate safeguards selected and allocated based on assessed risk levels and organisational priorities.
What Are the Key Steps in the ISO 27001 Risk Management Process?
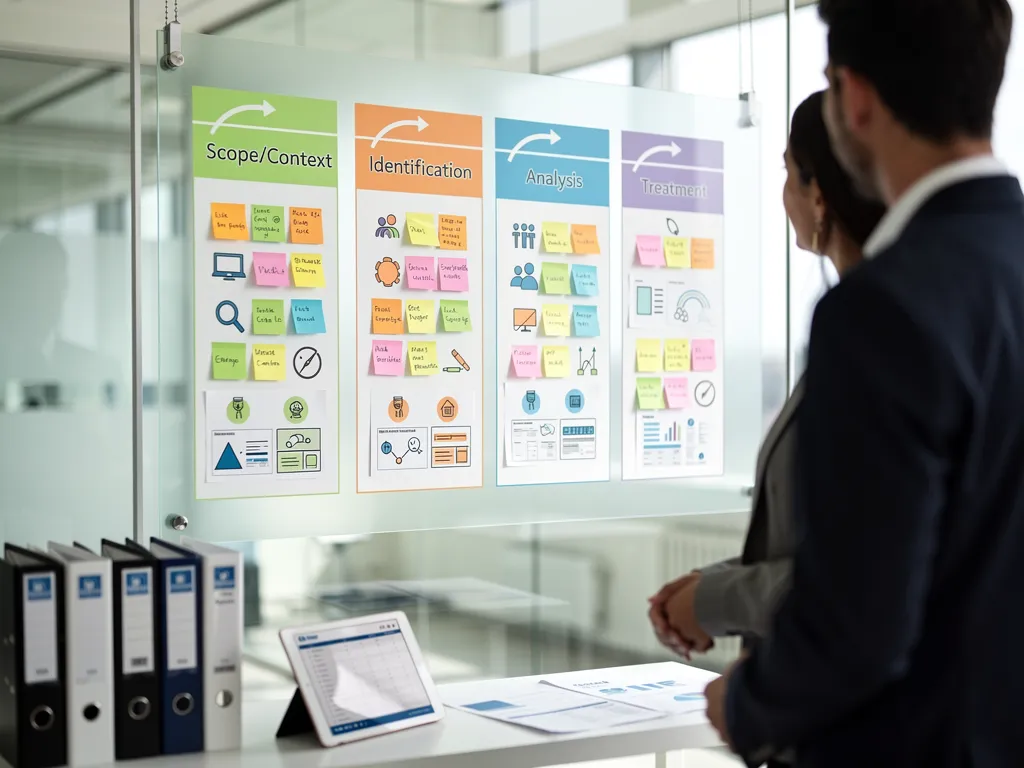
ISO 27001 prescribes a repeatable five-step risk management process: scope and context, identification, analysis, evaluation, and treatment—each producing specific, auditable deliverables. This structured flow ensures that risk decisions are consistent with business objectives and documented for auditors and stakeholders, tying the ISMS lifecycle to continual improvement through monitoring and review. Practical tooling for these steps includes an asset register, templated risk register fields, scoring matrices, and a maintainable Risk Treatment Plan aligned to Annex A controls. Implementing the process requires clear ownership at each step, evidence of stakeholder engagement, and periodic re-evaluation as threat landscapes evolve. The following numbered list summarises the five canonical steps for quick reference and featured-snippet style clarity.
Establish Scope & Context: Define boundaries, stakeholders, and risk criteria that guide assessment work.
Identify Assets, Threats & Vulnerabilities: Inventory assets, map threats (including AI/ML scenarios) and note vulnerabilities.
Analyze Risks: Estimate likelihood and impact using qualitative or quantitative methods.
Evaluate & Prioritize: Compare risk levels to acceptance criteria and rank for treatment.
Treat & Document: Select treatment strategies, create an RTP, and record choices in the SoA and risk register.
This ordered process produces clear artefacts—scope statement, asset inventory, risk register, RTP and SoA—that collectively demonstrate a controlled, repeatable approach to information security. The next table maps each step to its purpose and expected deliverable for quick scanning.
Phase | Purpose | Outcome / Deliverable |
|---|---|---|
Scope & Context | Define ISMS boundaries and risk criteria | Scope statement, stakeholders list, risk acceptance levels |
Identification | Find assets, threats, vulnerabilities | Asset register, threat catalogue, vulnerability log |
Analysis | Assess likelihood and impact | Risk register entries with scores and rationale |
Evaluation | Determine priority against criteria | Prioritised risk list with accepted/treated flags |
Treatment | Implement or plan controls | Risk Treatment Plan (RTP), updated SoA |
Introductory mapping of the canonical steps clarifies responsibilities and outcomes, helping teams translate process steps into documents auditors expect.
How to Define the Risk Assessment Scope and Context?
Defining scope and context requires listing organisational boundaries, critical processes, information flows and legal/regulatory drivers, and then aligning them with risk criteria such as impact levels and tolerances. Start with a concise scope statement that names systems, business units and locations in scope and excludes areas with justification, and capture external factors like supplier relationships or regulatory obligations that affect risk. Engaging stakeholders—IT, legal, HR, operations—ensures the context reflects business realities and that risk criteria are realistic and accepted. Practical tips include using process maps to visualise information flows and documenting assumptions about threat actors, which speeds later analysis and reduces review cycles.
How to Identify Assets, Threats, and Vulnerabilities?
Asset identification combines inventorying data, systems, people and suppliers and assigning value attributes such as confidentiality, integrity and availability priorities. Threat assessment then uses threat libraries and scenario workshops to capture probable events—phishing, credential theft, supply-chain compromise, and AI model poisoning—and maps them to assets. Vulnerability assessment uses scans, configuration reviews and control questionnaires to find weaknesses that enable threats to materialise. Use an asset catalogue with owner, location, classification and criticality to link assets to threats and vulnerabilities and populate the risk register efficiently.
How Are Information Security Risks Analyzed and Evaluated in ISO 27001?
Risk analysis in ISO 27001 translates identified scenarios into risk levels by combining likelihood and impact estimates and applying chosen scales or models, enabling prioritisation for treatment. Organisations select qualitative methods (risk matrices, scales) or quantitative techniques (annualised loss expectancy, statistical models) depending on available data and maturity; both aim to produce defensible rankings for management decisions. Rules for calculating likelihood and impact must be documented so reviewers understand why a risk is rated high or low; this traceability is crucial for audits. The table below helps teams choose an analysis technique by listing data requirements and trade-offs.
Technique | Data Required | Strengths / Weaknesses |
|---|---|---|
Qualitative matrix | Expert judgement, simple scales | Strength: fast and accessible. Weakness: subjective variance |
Quantitative modelling | Historical loss data, frequency rates | Strength: precise prioritisation. Weakness: data-hungry and complex |
Hybrid scoring | Mix of metrics and judgement | Strength: pragmatic balance. Weakness: requires discipline in calibration |
This comparison shows that SMEs often rely on qualitative or hybrid approaches for speed, while larger organisations benefit from quantitative modelling; next, we show how to score likelihood and impact practically.
Evaluating ISO 27001 Framework Effectiveness: A Quantitative Analysis This thesis quantitatively evaluates the effectiveness of cybersecurity measures by analysing threat types and the implementation of NIST and ISO 27001 frameworks. The study investigates how various cybersecurity threats, including malware and Advanced Persistent Threats (APTs), impact stakeholders in the digital age. It explores the efficacy of widely adopted frameworks like NIST and ISO 27001 in mitigating these threats and examines the role of human factors in cybersecurity. Using secondary data from reputable sources, the research provides a comprehensive assessment of the dynamic cybersecurity landscape, contributing valuable insights for businesses, governments, and policymakers to enhance their cybersecurity strategies.
What Risk Analysis Techniques Are Used: Qualitative vs Quantitative?
Qualitative techniques use descriptive scales (low/medium/high) and risk matrices to map likelihood against impact, suitable when historical data is scarce and rapid decisions are needed. Quantitative techniques calculate numeric estimations such as annualised loss expectancy (ALE) using incident frequency and expected loss values, which supports cost-benefit analysis of controls. Hybrid approaches combine qualitative judgement with measurable indicators (e.g., downtime minutes, number of affected records) to give clarity without the heavy data requirements of full quantitative models. Choose the approach that balances precision with practicality and document assumptions to retain auditability.
How to Calculate Risk Likelihood and Impact for Prioritization?
Calculate risk by assigning likelihood and impact scores using defined scales and then applying a formula—commonly Risk = Likelihood × Impact—to derive a risk rating that maps to priority levels. For example, a medium likelihood (3/5) and high impact (4/5) result in a score of 12, which an organisation may classify as high priority requiring mitigation. Include qualitative rationale alongside numeric scores so reviewers understand contextual factors like existing compensating controls. Use worked examples in the risk register to demonstrate consistency, and map rating thresholds to treatment actions such as immediate mitigation, monitored acceptance, or transfer.
What Are the ISO 27001 Risk Treatment Options and Documentation Requirements?
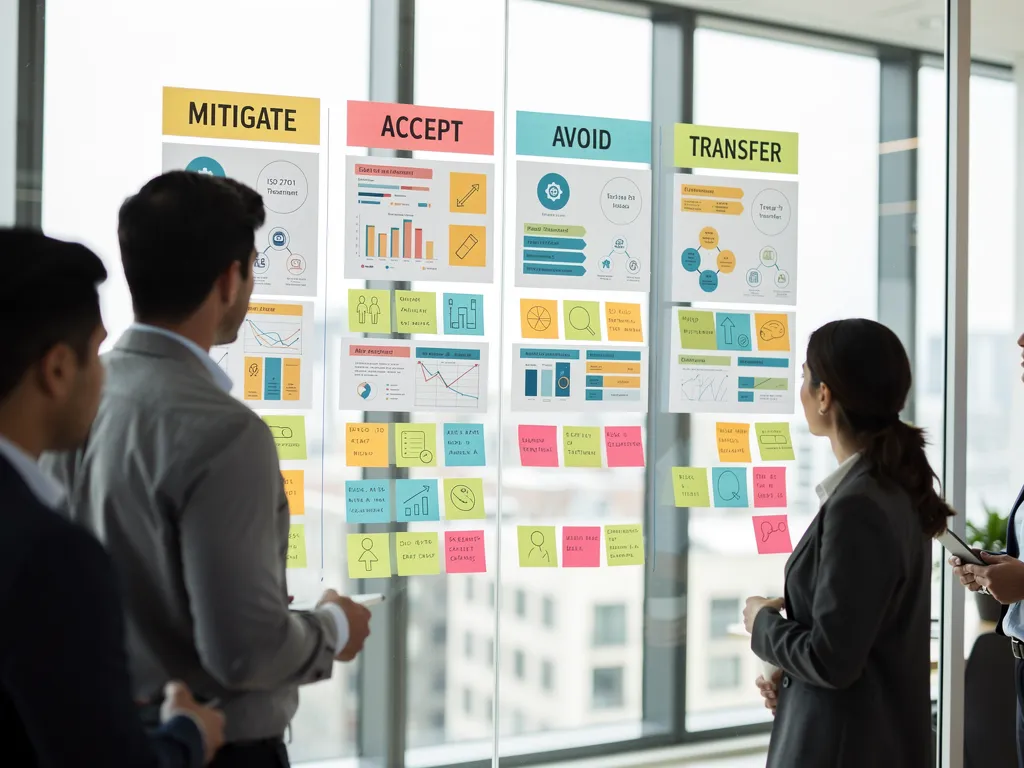
ISO 27001 identifies four primary risk treatment strategies—mitigate (modify), accept (retain), avoid, and transfer—and requires structured documentation of chosen approaches in a Risk Treatment Plan and a Statement of Applicability. The RTP defines specific actions, owners, timelines and metrics for each treated risk, while the SoA lists Annex A controls, records whether each control is implemented, and justifies inclusions or exclusions. Organisations map treatments to Annex A controls where mitigation is chosen and record compensating controls when standard controls are impractical. Below is a concise comparison of treatment options and when they are appropriate.
Treatment Option | When to Use | Example Controls / Actions |
|---|---|---|
Mitigate (Modify) | To reduce likelihood/impact to acceptable level | Implement backup and restore, access controls, patching |
Accept (Retain) | When cost of treatment outweighs benefit or risk is low | Documented acceptance, monitoring plan |
Avoid | When risk source can be eliminated or activity stopped | Discontinue risky service, decommission legacy system |
Transfer | To shift risk to third party or insurer | Contractual SLAs, cyber insurance, managed security services |
This table clarifies how each option maps to concrete actions; the following list summarises practical tips for choosing a strategy.
Prefer mitigation where controls materially reduce business impact and are cost-effective.
Retain only low-level risks with documented acceptance and monitoring.
Avoid when business benefit is minor and risk cannot be controlled efficiently.
Transfer when specialised third-party controls or insurance better manage residual exposure.
A well-structured RTP ties chosen strategies to Annex A references and measurable milestones; the next subsection describes RTP and SoA content and best practices.
What Are the Four Risk Treatment Strategies in ISO 27001?
The four strategies—mitigate, retain, avoid and transfer—cover all practical responses to assessed risks and must be applied consistently with documented rationale. Mitigation selects controls from Annex A or alternative safeguards to lower likelihood or impact and is the most common choice for technical and process risks. Retention is acceptable when risk falls within organisational tolerance and must include monitoring triggers; this option is typical for negligible operational risks. Avoidance removes the activity that creates the risk, useful when a process change is simpler than control implementation. Transfer shifts responsibility, often through contracts, cloud providers, managed services or insurance; choose transfer only when contractual controls are explicit and enforceable.
How to Develop a Risk Treatment Plan and Statement of Applicability?
Developing an RTP starts with a prioritised risk list, assigns owners and target dates, and specifies measurable controls and verification steps; it becomes a live project tracker for remediation. The SoA should list each Annex A control, state its applicability, describe implementation status and provide justification for exclusions—this creates audit evidence linking identified risks to selected controls. Best practices include aligning RTP milestones with resource planning, using control mapping templates to Annex A, and versioning both RTP and SoA so auditors can trace changes over time. Regularly review and update the RTP when risk ratings change or when new controls are implemented to maintain certification readiness.
How Does Continuous Improvement and Monitoring Enhance ISO 27001 Risk Assessment?
Continuous improvement and monitoring ensure the ISMS remains effective as threats, technology and business processes evolve, turning a one-off assessment into a living risk management process. Monitoring activities include scheduled risk reviews, automated alerts from security tools, supplier assurance checks and periodic reassessment after significant changes such as new AI/ML deployments. Internal audits and management review provide formal mechanisms to assess the ISMS’s performance, verify controls, and prioritise improvements based on evidence. Embedding automation and threat intelligence accelerates detection and helps incorporate emerging threats—like AI model misuse—quickly into the risk register and treatment plans. The following list describes practical monitoring and review approaches teams should adopt.
Scheduled risk reviews: Quarterly or event-driven re-evaluations of high-priority risks.
Continuous monitoring: Use logging, alerting and SIEM outputs to detect changes affecting risk.
Supplier assurance: Regular checks and questionnaires to monitor third-party risk posture.
Threat intelligence: Subscribe to feeds and translate relevant indicators into register updates.
Taken together, these practices close the loop between detection, assessment and treatment and keep the ISMS resilient and audit-ready. The next table summarises recommended review cadences and evidence types auditors look for.
Review Activity | Recommended Cadence | Audit Evidence |
|---|---|---|
Risk register review | Quarterly or after major change | Updated register with dated entries |
Internal audit | Annual or rotation-based | Audit reports, corrective action records |
Management review | At least annually | Meeting minutes, action trackers |
Supplier reassessment | Annual or SLA-triggered | Supplier questionnaires, contracts |
This schedule supports demonstrable continual improvement and shows auditors that risk assessment is a dynamic, managed process.
ISO 27001 Risk Management for Health Services: A Case Study To find out the possible risks that can occur at PMI, the ISO 31000: 2018 method is used and the control standard uses ISO 27001: 2022. It can be seen from the 22 possible risks, there are 4 possible risks with very high levels, 2 possible risks with high risk levels, 10 possible risks with moderate risk levels, and 6 possible risks with low risk levels. The control recommendations
How to Conduct Regular Risk Reviews and Internal Audits?
Regular reviews require a clear schedule, defined roles and documented evidence of findings and actions; assign a risk owner for each major risk and set review triggers based on control performance or incidents. Internal audits should follow an audit plan that samples risk processes, verifies RTP progress and checks SoA consistency; auditors record findings and corrective actions with owners and deadlines. Use standard checklists to ensure consistent evidence collection—logs, change records, training records and RTP status all serve as audit artefacts. Effective reviews culminate in management review meetings that translate audit findings into resourcing and strategic decisions.
How to Monitor Emerging Threats and Update the ISMS?
Monitoring emerging threats combines feeds from reputable intelligence sources, supplier risk signals, incident post-mortems and internal telemetry to identify new scenarios for the risk register. For AI/ML risks, map potential failure modes—data poisoning, model leakage, adversarial inputs—into asset-threat pairs and estimate their likelihood and impact using expert judgement and testing results. When a new threat is identified, log it with an owner, rate it against criteria and trigger RTP updates where mitigation is required. Ensure that every register update includes rationale and evidence so auditors can trace why and when the ISMS was altered.
How Can ACATO Support Your ISO 27001 Risk Assessment and Certification Journey?
Provide useful information and expertise to lead potential clients to book free consultations or engage their services. ACATO specialises in ISO 27001 consulting and end-to-end readiness support, helping organisations run gap analyses, develop ISMS documentation, and prepare for certification audits with practical, hands-on guidance. Their services include tailored risk assessment facilitation, creation of risk registers and Risk Treatment Plans, mapping Annex A controls and drafting Statements of Applicability to align with audit expectations. ACATO also offers IT security consulting, security audits, digital forensics and incident response services which complement risk treatment activities and aid in forensic readiness where incidents occur. Engaging such specialists reduces time-to-certification and alleviates common frustrations by providing templates, evidence frameworks and experienced advisors to guide remedial projects.
What Expert Services Does ACATO Provide for Risk Assessment?
ACATO provides core services relevant to ISO 27001 risk assessment including gap analysis to identify compliance shortfalls, ISMS documentation development to produce scope statements and procedures, and hands-on audit preparation to align evidence with auditor expectations. Their practical deliverables often include a populated risk register, a Risk Treatment Plan with owners and timelines, and a Statement of Applicability mapped to Annex A controls. Additional offerings such as IT security audits, digital forensics and incident response bring specialised capabilities that help organisations test controls, investigate incidents and strengthen overall resilience.
What Are the Benefits of Partnering with ACATO for ISO 27001 Compliance?
Partnering with ACATO delivers clear benefits: expert guidance that reduces time and frustration during preparation, structured templates and documentation that streamline evidence collection, and an integrated approach that connects ISO 27001 risk management with GDPR and forensic readiness. Clients gain practical support for gap closure and audit readiness, access to specialists for incident response and forensic analysis, and a partner focused on rapid, measurable progress toward certification. For organisations that prioritise efficient readiness and expert advice, ACATO’s services provide a pragmatic route to sustained ISMS effectiveness and audit confidence.